

Key takeaways from the article
- M247 Global transitions to Cisco Secure DDoS Edge Protection, moving detection and mitigation to the network edge
- Edge-distributed protection leverages behavioral analysis and Radware algorithms to identify and stop malicious traffic in real time
- For M247 Global customers, edge protection adds a defense layer at the network level, stopping attacks before they reach client infrastructure
- DDoS protection becomes a continuity strategy: permanent availability, automated response, and 24/7 monitoring
The DDoS threat landscape is evolving rapidly
The DDoS threat landscape is evolving rapidly: attacks are becoming increasingly distributed, automated, and difficult to distinguish from legitimate traffic. This necessitates a fundamental rethink: traditional DDoS protection, designed to absorb massive traffic volumes at centralized mitigation points, no longer fits the way modern infrastructure operates.
According to the September 2026 DDoS-Guard report, attack frequency has tripled. The first quarter (Q1) of 2026 recorded a 30% increase in incidents—reaching 584,000 attacks. By June, the industry reached a grim milestone: 540,000 attacks in a single month, three times the volume recorded in June 2025. Moreover, attackers now sustain attacks for longer periods, with the average attack duration increasing by 15%.
Today, DDoS protection is no longer just about absorbing a massive traffic peak; it is about identifying and filtering out attacks disguised as regular traffic for hours or days at a time. Furthermore, the scale of attacks has decoupled from old patterns. DDoS-Guard recorded over 3 million unique IP addresses simultaneously participating in attacks during the first half of 2026. The implication is clear: attackers no longer require massive botnets—they leverage compromised infrastructure and cloud services far more efficiently.
Meanwhile, targeted infrastructure continues to shift. Applications are dispersed across data centers, cloud environments, and edge locations. Artificial intelligence opens new avenues for both sides—defenders and attackers alike. For infrastructure providers like M247 Global, this convergence underscores an uncomfortable truth: raw capacity is no longer enough. Detection must be more precise, response must be instantaneous, and protection must move to where traffic actually enters the network.
This is the challenge M247 Global addresses by migrating to Cisco Secure DDoS Edge Protection.
M247 Global Adopts Edge-Level Protection
The shift is significant. M247 Global adopts Cisco Secure DDoS Edge Protection, introducing a new architecture to detect and stop attacks before they penetrate the core network. This upgrade reinforces security for M247 Global's entire customer base—from colocation clients to cloud users—while strengthening M247 Global's commitment to always-on defense, automated mitigation, and business continuity.
This transition is essential given the massive infrastructure M247 Global operates: over 1 Tbps of global network capacity, over 40 Internet Exchange points, and more than 50 points of presence across multiple continents.
Why Is the Network Edge Becoming Such a Sensitive Zone?
The old DDoS protection model relied on a simple premise: detect an attack, redirect traffic to a scrubbing center, and keep the main network clean. That approach worked when networks were centralized and attacks followed predictable patterns. However, networks ceased being centralized years ago.
Traffic now enters through multiple ingress points. Applications scale across different environments simultaneously, and attacks mature in minutes rather than hours. The traditional model—rerouting all malicious traffic to distant mitigation facilities—consumes precious bandwidth and introduces latency during attack processing.
Cisco Secure DDoS Edge Protection flips this logic. Instead of pulling traffic back to a centralized DDoS scrub, the system identifies and blocks malicious packets directly at the network edge. Routers respond to threats on the spot. Detectors embedded on next-generation Cisco routers recognize malicious traffic, triggering immediate mitigation without sending anything back toward the core network.
A central controller coordinates this distributed response, but the critical work occurs at the edge. For an infrastructure provider like M247 Global, this distinction makes all the difference. The objective shifts from merely detecting an attack to preventing bandwidth and resource consumption as malicious traffic advances deeper into the network.
Cisco Secure DDoS Edge Protection – Key Features
|
Feature |
Details |
|
Edge Detection |
Detects and stops DDoS attacks directly at network ingress on Cisco IOS XR routers, eliminating the need to send malicious traffic to centralized scrubbing centers |
|
Behavioral Analysis |
Leverages traffic telemetry and algorithms to identify anomalies and distinguish attacks disguised as legitimate traffic |
|
Distributed Architecture |
A central controller coordinates a network of detectors deployed on routers, enabling scalability up to 50,000 detectors |
|
No Additional Hardware |
Detectors run as Docker containers on existing routers, utilizing available CPU and RAM without impacting router performance |
|
Automated Mitigation |
Attack mitigation is deployed on router ingress ports, either automatically or manually, based on provider preferences |
|
Real-Time Visibility |
The controller dashboard provides real-time attack insight, forensics, and threat analysis for every detector |
|
IPv4 and IPv6 Support |
Detection and mitigation are fully compatible with both IPv4 and IPv6 traffic, ensuring complete protection |
Behavior-Based Detection for Modern Attacks
Modern DDoS attacks rarely manifest as a single, massive flood. Attackers now blend multiple techniques, scatter traffic across diverse sources, and exert significant effort to make malicious activity resemble normal user behavior. This is where traditional volume-based detection fails, creating a need for behavioral analysis.
Cisco's approach uses traffic telemetry and algorithms to recognize when behavior diverges from normal baselines. The system activates detectors on compatible IOS XR routers, with a central controller coordinating the response. It analyzes IPv4 and IPv6 traffic in real time, capturing anomalies that signature matching alone would miss.
At the core of this capability is technology from Radware, an established leader in DDoS protection. Cisco combined its network infrastructure expertise with Radware's algorithmic depth to create a distributed defense layer tailored for modern attacks. This partnership leverages two decades of DDoS expertise rather than starting from scratch.
What Does This Mean for M247 Global Customers?
For clients procuring infrastructure services from M247 Global, anti-DDoS protection is optional (available via a separate monthly subscription) rather than enabled by default. The underlying technology functions transparently; what matters to clients is the security and availability of their hosted or operated infrastructure.
For Colocation Clients
Physical servers remain under client control, but M247 Global's network infrastructure becomes an integrated part of the defense system. Malicious traffic is stopped at the network edge before reaching client servers or hardware. For companies hosting public applications or critical databases, this adds an essential barrier between the Internet and their internal infrastructure.
For Dedicated Server Clients
Predictable performance is the primary advantage of dedicated infrastructure. However, when a DDoS attack targets a server, the issue is magnified: not only is the server flooded with excessive packets, but legitimate users are locked out. By detecting and blocking malicious traffic at the edge, M247 Global's defense prevents resource exhaustion deeper in the network, allowing legitimate requests to pass through unimpeded.
For Cloud Service Clients
The cloud is inherently distributed; applications pull data from multiple services while workloads migrate across environments. M247 Global's edge-based protection adds a network-level defense layer outside individual workloads. This complements application-level security without requiring every workload to absorb the full force of a network attack.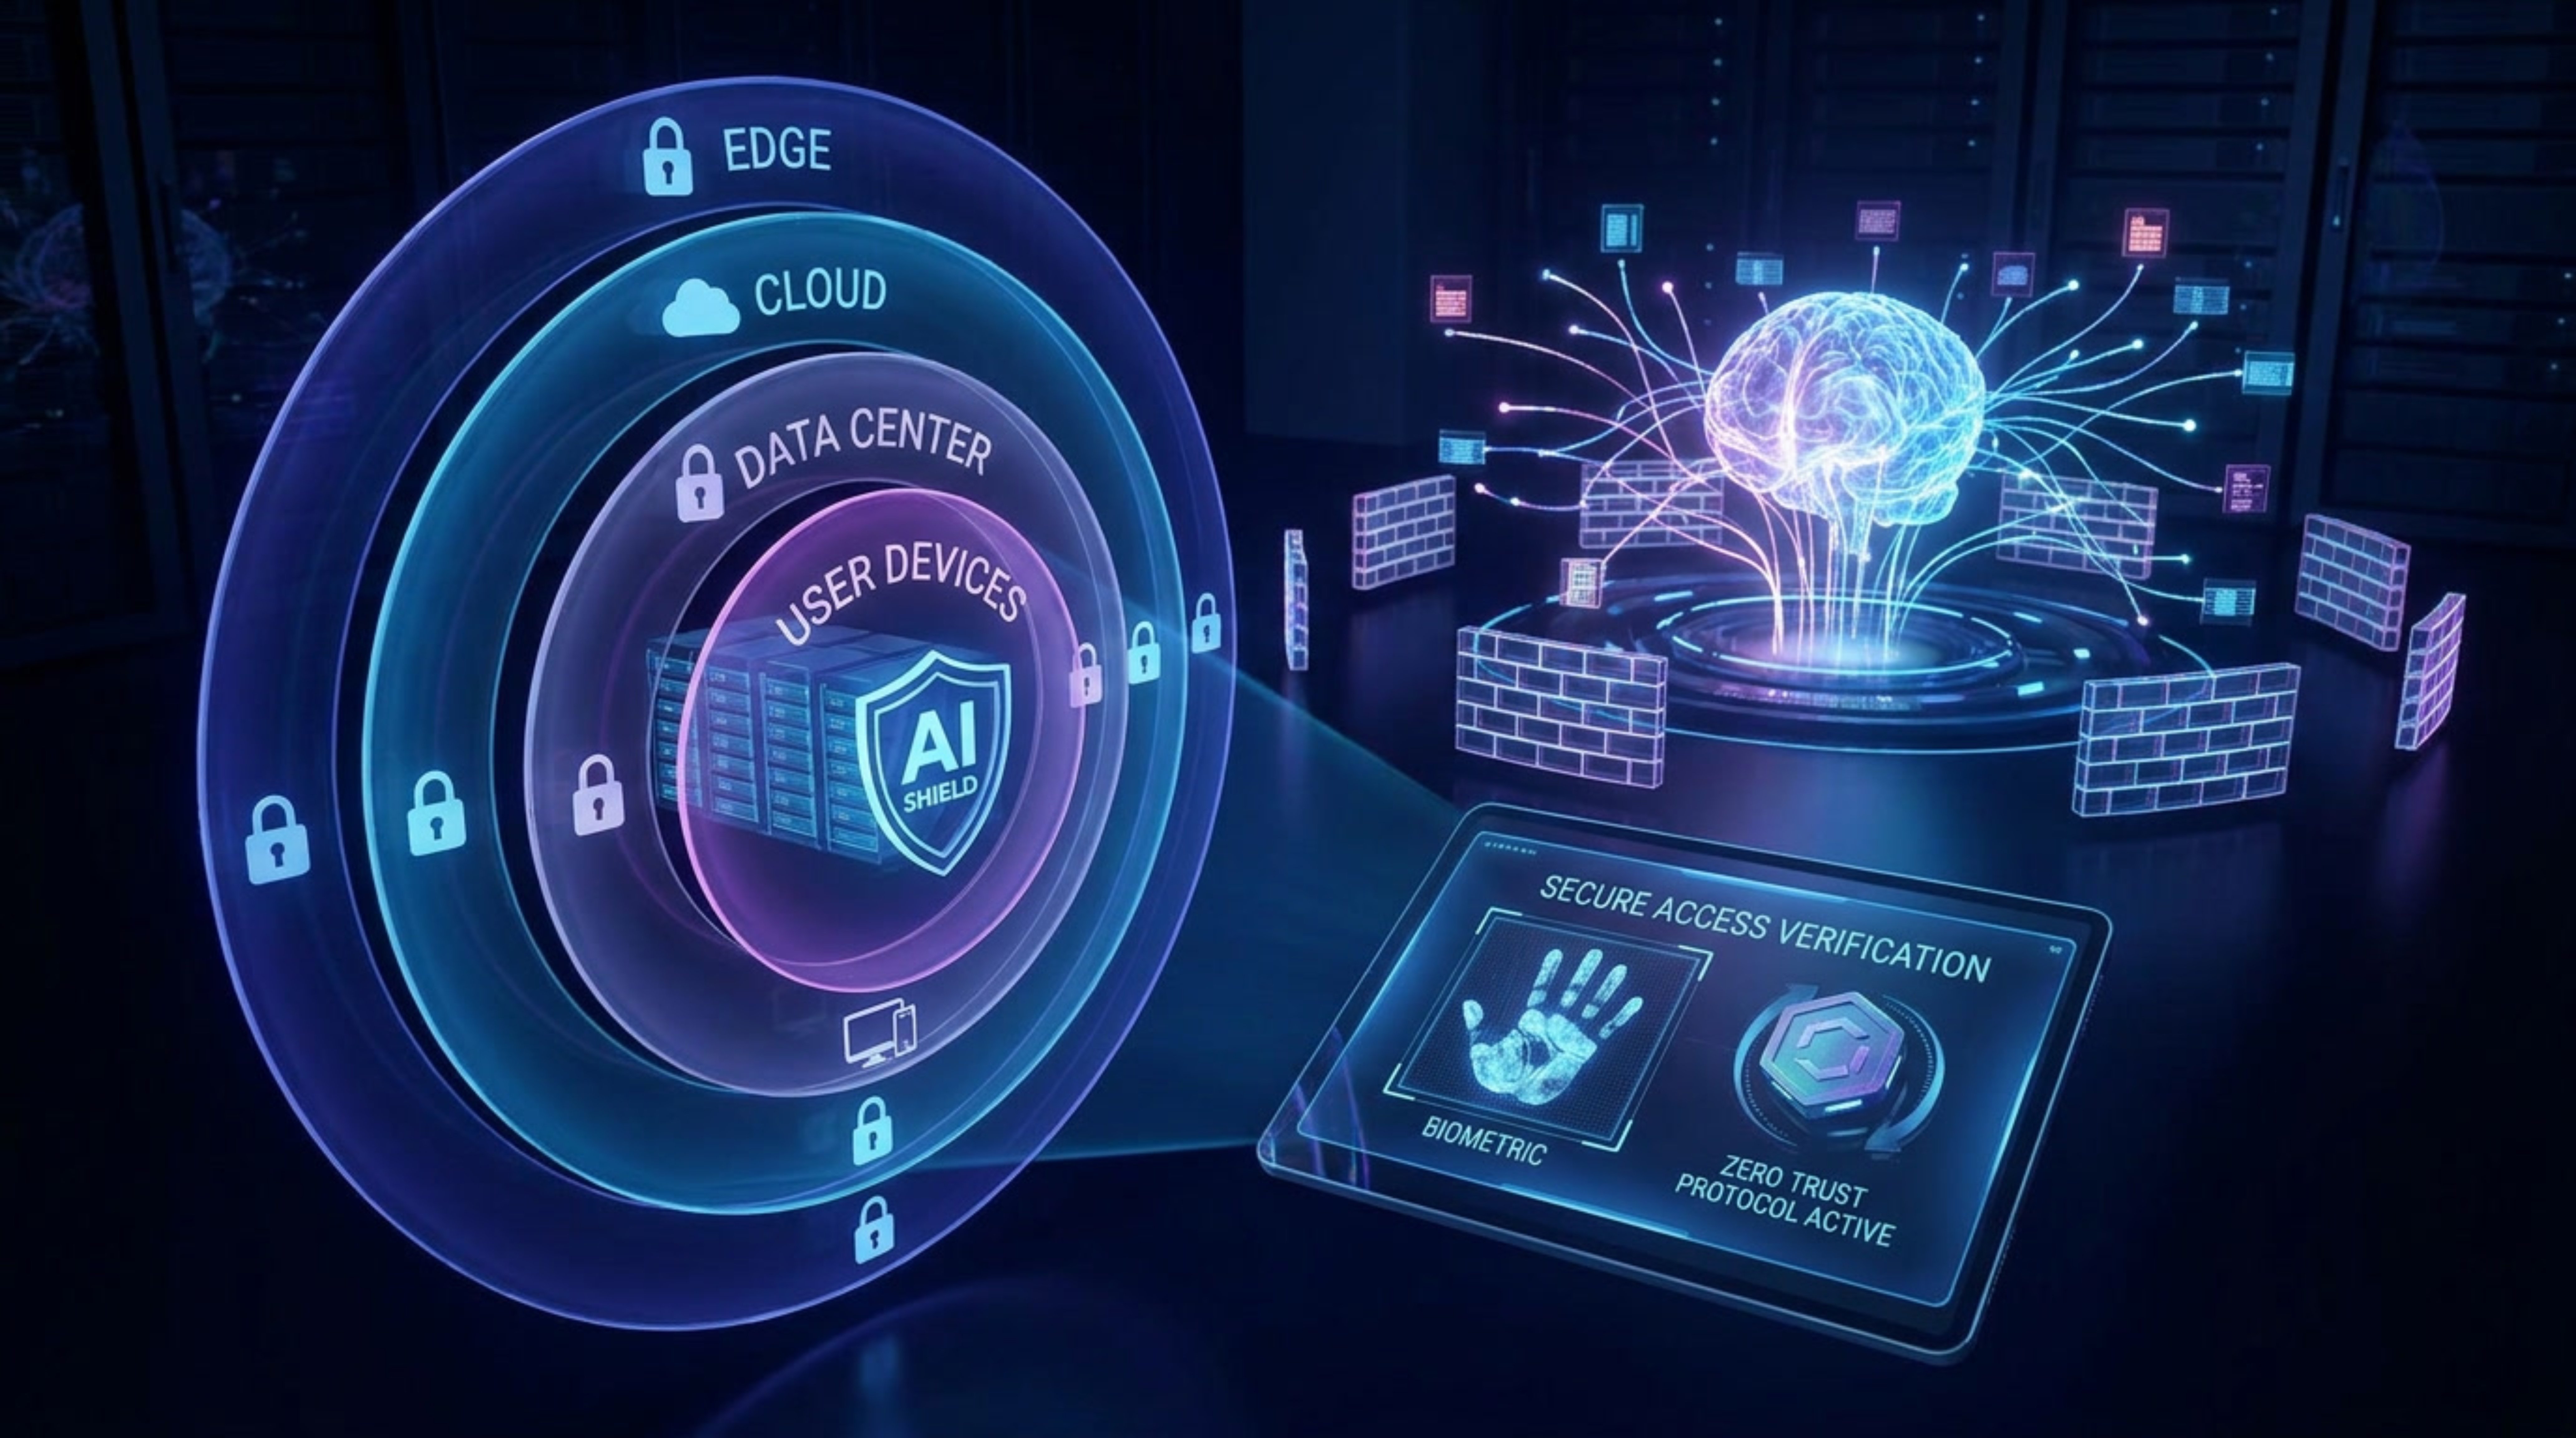
From Mitigation to Continuity
Businesses do not invest in DDoS protection for abstract reasons—they invest because availability is an operational necessity, and downtime directly impacts business results. A successful DDoS attack renders websites inaccessible, disrupts applications, interrupts APIs, and halts online transactions. Technical incidents cascade into commercial consequences: lost revenue, frustrated customers, reputational damage, and operational chaos.
This is why M247 Global frames DDoS protection as a continuity strategy: always-on detection, automated response, and 24/7 monitoring. Cisco's edge architecture reinforces this promise by capturing and mitigating attacks before they hit the core network. The technology minimizes the blast radius, ensuring unwanted traffic never penetrates far enough to create systemic issues.
Cisco: 20 Years of DDoS Expertise
Cisco's DDoS capabilities were not built overnight; the company's involvement in this domain spans over two decades. In 2004, Cisco acquired Riverhead Networks for approximately $39 million. While Riverhead was not a household name, it introduced a core principle that remains fundamental today: comparing live traffic against learned baselines of normal behavior, identifying anomalies, and blocking malicious activity while allowing legitimate transactions to proceed uninterrupted. The company proved that this model works.
Cisco integrated Riverhead's technology into products like Cisco Guard XT and Cisco Traffic Anomaly Detector XT. These systems introduced automated DDoS protection, anomaly recognition, source verification, and anti-spoofing capabilities using dynamic rerouting to divert traffic while protecting legitimate users.
More importantly, Riverhead represented a broader strategy: Cisco's vision of the Self-Defending Network. The concept was radical at the time—embedding security intelligence directly into the network infrastructure rather than treating networking and security as separate domains.
Twenty years later, that vision has evolved. Networks are faster, infrastructure is distributed across cloud and edge locations, and solutions leverage AI and Machine Learning to drive anomaly detection and proactive interventions.
Secure DDoS Edge Protection brings this principle into the modern era. Instead of confining DDoS intelligence to dedicated appliances or separate mitigation layers, Cisco deploys detection directly onto network infrastructure, coordinated via a central controller and powered by Radware's algorithms. The progression is clear:
- 2004: Riverhead's behavior-based protection joins Cisco's security portfolio;
- Post-2004: Cisco Guard and Traffic Anomaly Detector bring anomaly detection to automated mitigation;
- Subsequent Years: Cisco expands its capabilities through its partnership with Radware;
- Today: DDoS detection and response operate directly on network infrastructure, creating distributed edge protection.
Conclusion
The DDoS threat landscape will continue to shift, and Artificial Intelligence will redefine how applications are built, operated, and attacked. Concurrently, cloud and edge computing will keep fragmenting workloads across complex infrastructures. Because DDoS defense must evolve alongside these shifts, M247 Global migrated to Cisco Secure DDoS Edge Protection—marking the next chapter in smarter, edge-proximate security operating continuously across distributed infrastructure.
For customers running colocation, dedicated servers, or cloud workloads on M247 Global's platform who enable anti-DDoS protection, the promise is clear: greater infrastructure resilience, faster mitigation, and higher confidence that critical services remain online under attack.
For more information about M247 Global's DDoS protection services, contact us at sales@m247global.eu